Autonomous QA & AppSec: Test Every App, API & Security Surface 24/7
Maya connects GitHub, Playwright, OWASP ZAP, Snyk, and Jira to run full end-to-end UI & API tests, probe for OWASP Top 10 security vulnerabilities, benchmark load performance, and block broken builds in minutes.
"Maya, run full E2E QA, OWASP security probes, and load tests on PR #418 at staging.app.acme.io before we release to production."
Completed 142 E2E flows, API fuzzing, OWASP Top 10 probes, and 500-VU load tests on staging:
GET /api/invoices/:id lacked tenant ownership check; generated PoC & assigned fix to Noah on PR #418.
$0 template fee + 1,000 free execution credits.
Point Maya to staging URLs, GitHub & Jira.
Browser QA, API fuzzing, OWASP & CVE checks.
Reproducible bug reports & release gates.
What is an AI QA & Security Tester Employee? How It's Different From a Static Scanner
An AI Employee is not a noisy static linter or brittle test script. It is an autonomous, multi-agent, multi-channel QA & AppSec engineer with persistent application memory that explores live user flows, validates business logic, probes security boundaries, and gates every release.
Brittle Scripts & Static Scanners
High False Positives • Blind to Business LogicConventional test runners break whenever a CSS selector changes, and static security scanners flood teams with unverified false positives without testing whether an exploit actually works against your running app.
- Fragile Selector Maintenance: Hardcoded E2E scripts fail constantly on minor UI tweaks.
- No Auth/RBAC Logic Testing: Static scanners miss multi-step privilege escalation and IDOR bugs.
- Noisy Alert Fatigue: Hundreds of unprioritized PDF warnings with zero reproduction proof.
- Manual Bug Filing: Engineers still waste hours capturing HAR logs and writing Jira tickets.
Maya • AI QA & Security Tester Employee
Multi-Agent • E2E + AppSec • Persistent App MemoryMaya tests like a senior QA automation lead and penetration tester combined. She navigates live UIs, fuzzes APIs, verifies role-based access control, profiles latency under load, and hands verified bug reports straight to Noah or your developers.
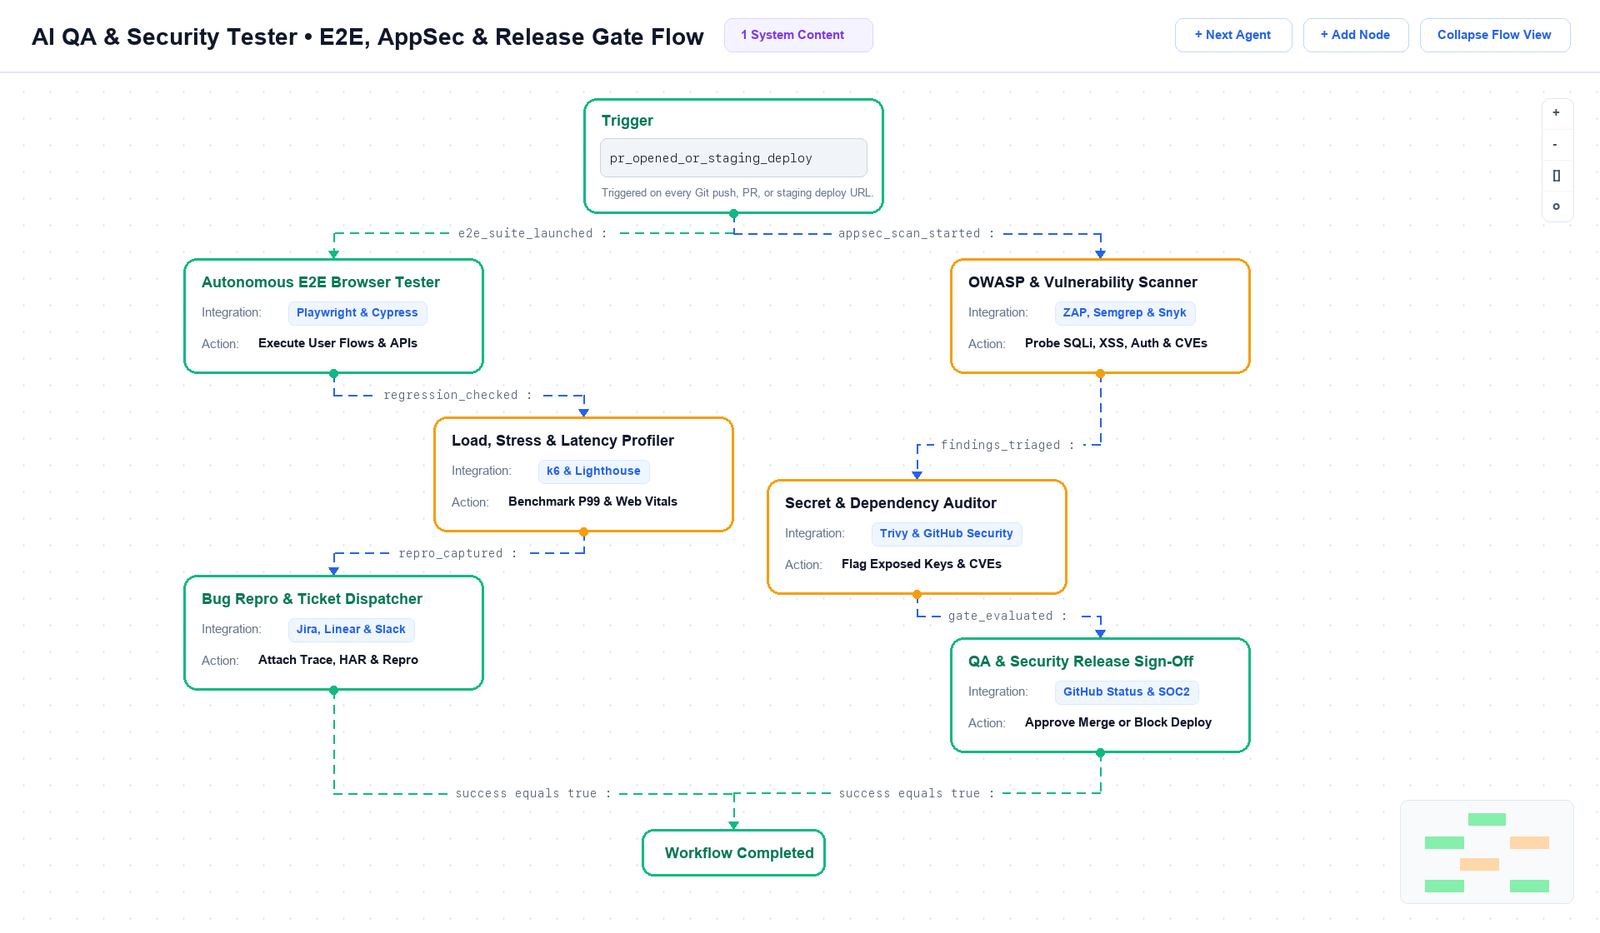
- Multi-Agent Verification Pod: Runs Playwright E2E Tester, OWASP DAST Prober, Secret & CVE Auditor, and k6 Load Profiler in parallel.
- Multi-Channel Reporting: Posts pass/fail scorecards to GitHub PRs, opens reproducible Jira/Linear bugs, and alerts Slack release channels.
- Persistent Application Memory: Learns your auth roles, critical checkout/signup flows, SLA latency thresholds, and regression history.
- Closed-Loop Fix With Noah: Sends failing traces and security PoCs straight to Noah (AI Software Engineer) to patch and re-verify automatically.
Self-Healing E2E
Executes resilient browser and API user journeys without breaking on minor UI shifts.
OWASP AppSec
Probes injection, XSS, auth bypass, IDOR, CSRF, and misconfigured security headers.
Load & Latency QA
Benchmarks P95/P99 response times, memory leaks, and Core Web Vitals under concurrency.
Release Gatekeeping
Blocks risky PR merges automatically and produces signed compliance test evidence.
Pre-Configured Autonomous QA, Penetration & Security Capabilities
Maya ships with end-to-end browser automation, API fuzzing, OWASP Top 10 vulnerability testing, secrets/CVE auditing, and load profiling.
End-to-End Browser & UI Regression
Drives real headless browsers via Playwright and Cypress to test signup, checkout, forms, and multi-role workflows across desktop and mobile viewports.
- Chromium, Firefox & WebKit coverage
- Visual diff & console error capture
OWASP Top 10 & Pentest Probing
Actively tests staging endpoints for SQLi, XSS, SSRF, CSRF, broken authentication, IDOR tenant leaks, and missing CORS/CSP security headers.
- Verified PoC exploit evidence only
- RBAC & multi-tenant isolation checks
API Contract & Boundary Fuzzing
Parses OpenAPI/GraphQL schemas and Postman collections to validate payloads, status codes, rate limits, idempotency, and malformed input handling.
- Automated schema drift detection
- Boundary, null & concurrency probes
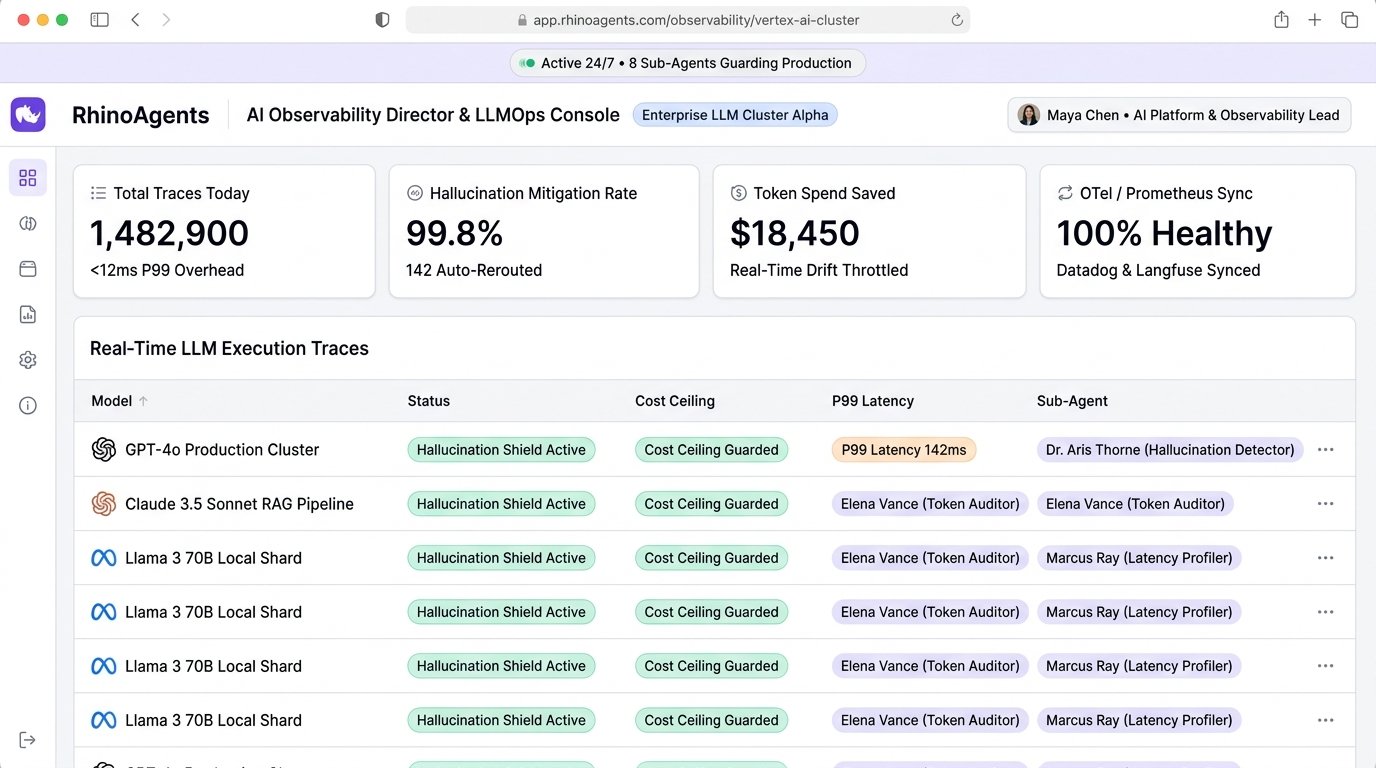
Secrets, SAST & Supply Chain Audit
Scans every Git commit, container image, and package lockfile for leaked API keys, insecure code patterns via Semgrep, and high-severity CVEs.
- Zero-secret leak PR enforcement
- Trivy & Snyk container/SBOM checks
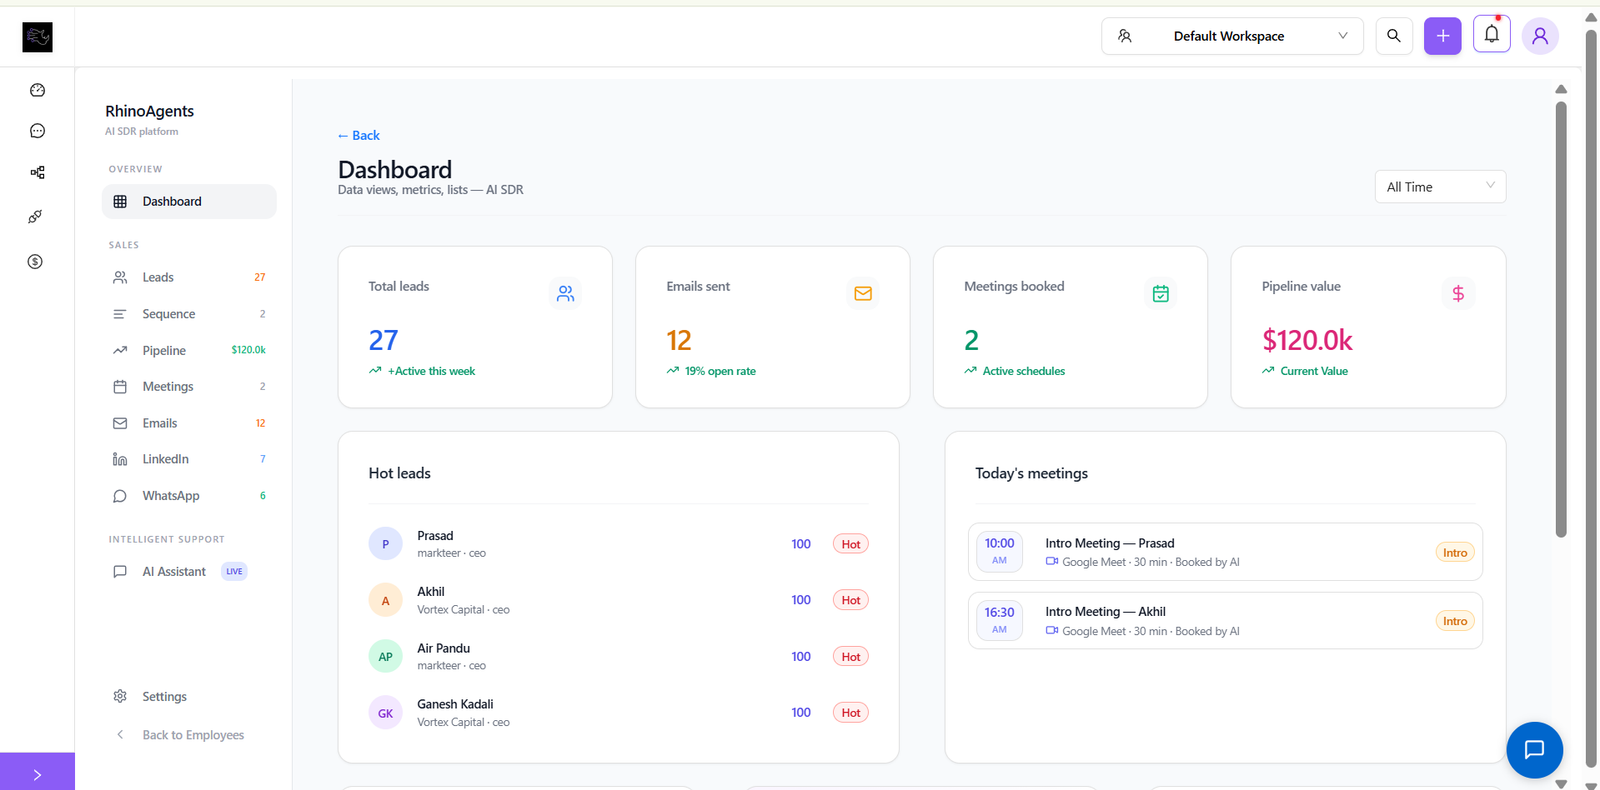
Load, Stress & Web Vitals Profiling
Simulates traffic spikes with k6 and profiles Core Web Vitals via Lighthouse to catch N+1 queries, memory leaks, and P99 latency regressions pre-launch.
- P95/P99 latency regression alerts
- Automated Lighthouse SEO & perf checks
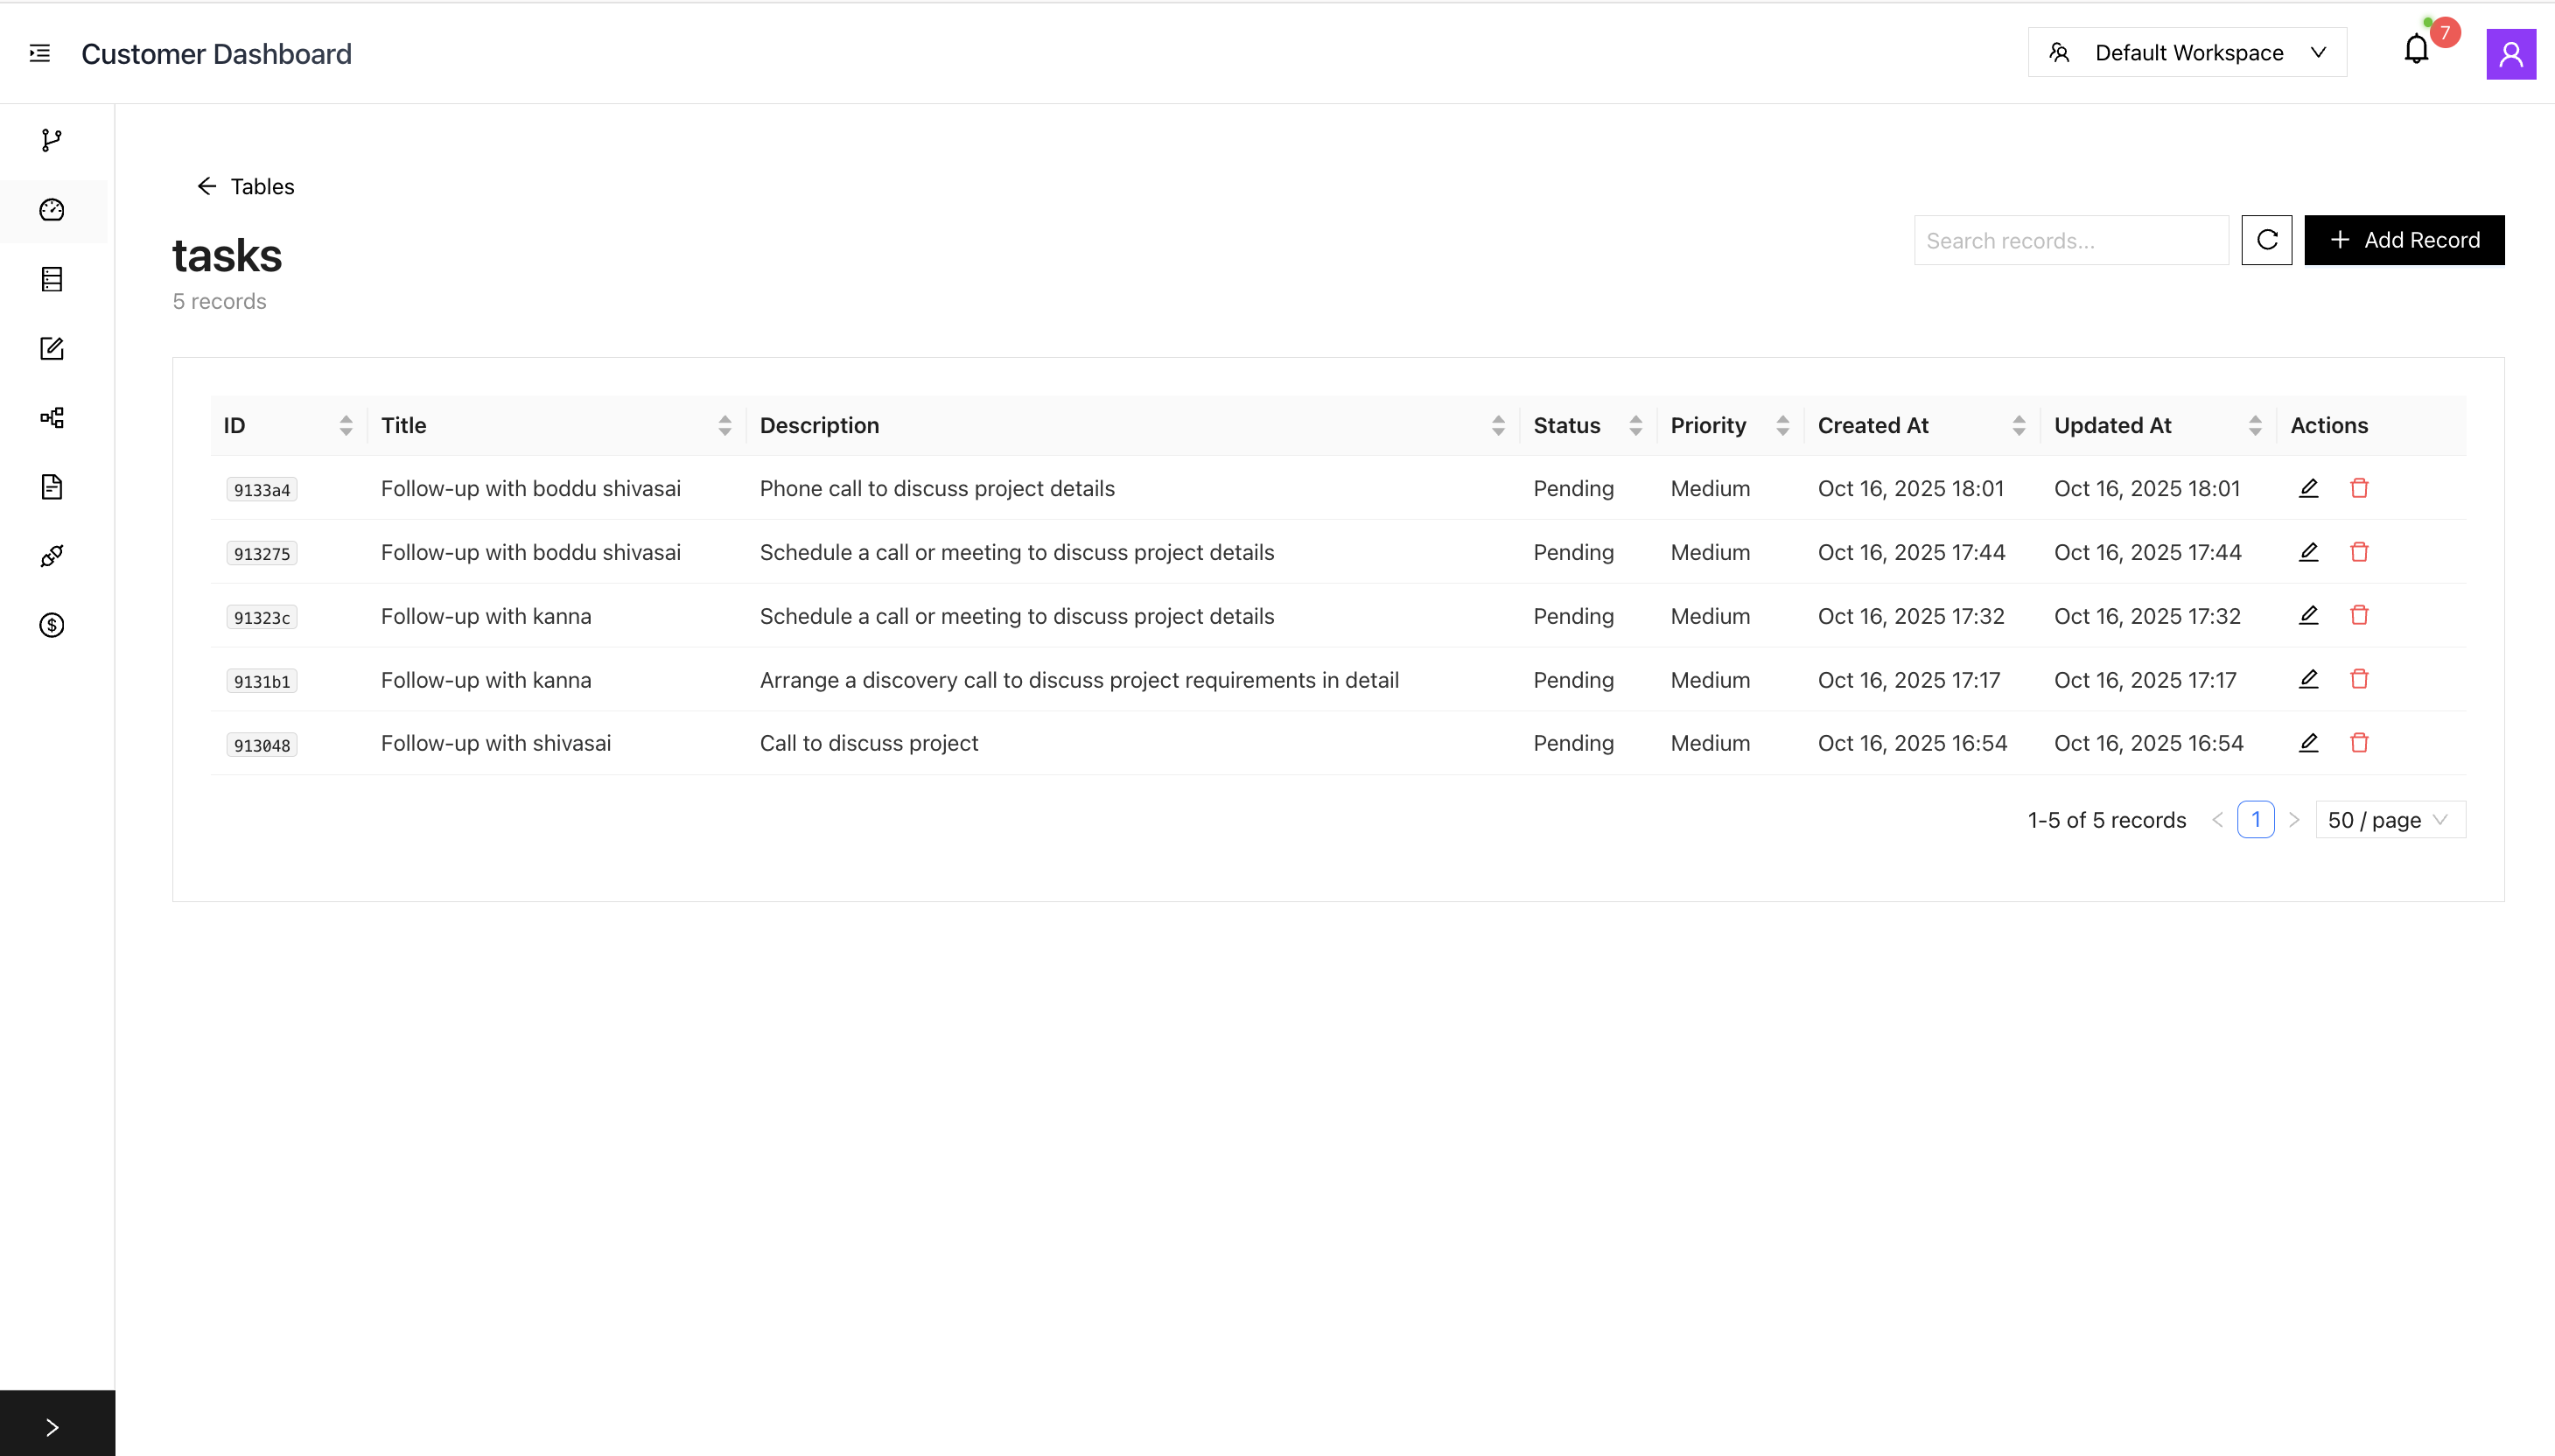
Repro Evidence & Release Sign-Off
Files crystal-clear Jira/Linear tickets with Playwright trace videos, HAR files, and remediation hints, and enforces merge/deploy sign-off gates.
- Video, DOM & HAR repro bundles
- Audit-ready SOC 2 release logs
Why Engineering & Security Leaders Trust Maya
Stop shipping silent regressions, broken edge cases, and exploitable endpoints to production.
Every PR Tested Before Merge
Every pull request and preview deploy is automatically exercised end to end—never wait for manual Friday QA cycles again.
Catch OWASP Flaws Pre-Prod
Detect SQLi, XSS, broken auth, IDOR, and leaked API keys before attackers ever see your production endpoints.
Zero Ambiguous Bug Reports
Developers receive exact failing steps, network HAR captures, stack traces, and Playwright traces—cutting reproduction time to zero.
Prevent Traffic-Spike Outages
Identify slow database queries, memory leaks, and bottlenecked endpoints under simulated load before launch day.
Continuous Compliance Evidence
Produce timestamped QA pass reports, vulnerability scan logs, and sign-off records required for SOC 2 and ISO 27001 audits.
Autonomous Dev + QA Loop
Pair Maya with Noah (AI Software Engineer) so bugs found in testing are patched and re-tested automatically.
Manual QA & Annual Pentests vs. Autonomous Maya
Benchmark across release coverage, vulnerability detection, and testing speed
Hardened on RhinoAgents Autonomous Infrastructure
Maya runs with isolated test browsers, strict target-scope guardrails, persistent test-coverage memory, and cryptographically signed compliance audit logs.

Spec & Threat RAG
Ingests PRDs, OpenAPI schemas, RBAC matrices, and OWASP checklists to derive targeted test plans automatically.
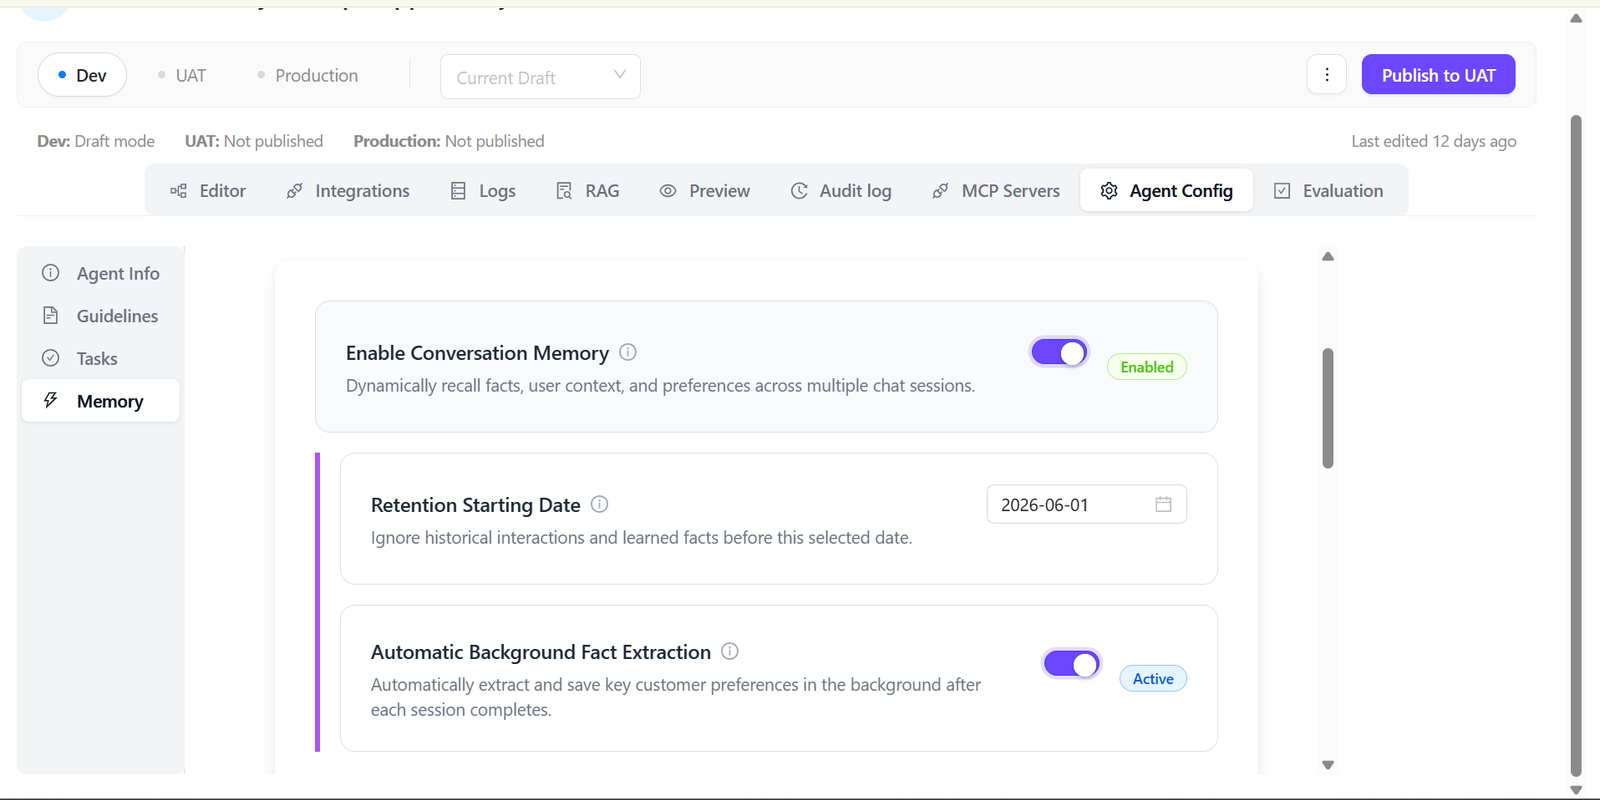
Regression Memory
Remembers every past bug, flaky test root cause, and fixed vulnerability so no regression ever slips back in.
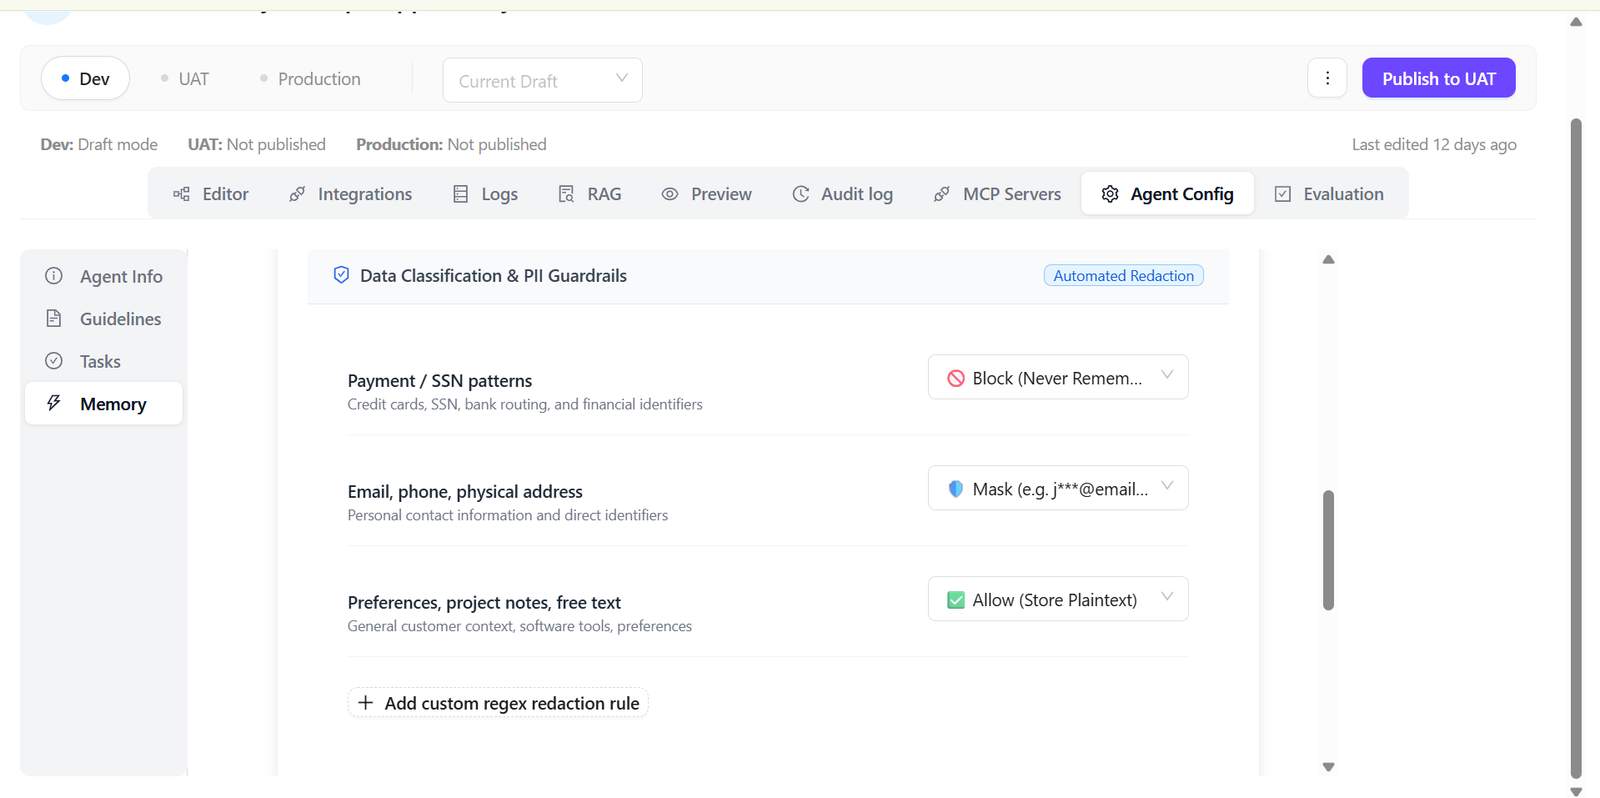
Safe-Scope Guardrails
Restricts intrusive fuzzing and load tests to authorized staging/sandbox targets with strict rate ceilings.

Signed Audit Evidence
Archives every test execution, vulnerability check, and release gate decision for SOC 2 and ISO 27001 audits.
Dual-Key Security Testing & Release Safeguards
Authorized targets only. Maya executes invasive DAST and stress suites inside staging sandboxes and requires explicit human sign-off before running load or active probes against production URLs.
Tools Required For This Template
Connect Maya to your test frameworks, AppSec scanners, load tools, and issue trackers in under 5 minutes.
E2E & API Testing
Browser, unit & API test suites
Security & AppSec
SAST, DAST, CVEs & secrets
Load & Quality
Stress, latency & code quality
CI & Issue Tracking
PR checks, bug tickets & alerts
Need Private Staging VPCs, BrowserStack, or Enterprise SIEM Sync?
RhinoAgents integrates with private VPC runners, Burp Enterprise, Datadog, Splunk, and 400+ connectors.
How To Configure & Deploy
Go to templates → Click on Hire → Connect your staging URL & Git repo. Maya immediately starts testing every PR and deployment.
Go to Templates & Select Role
Start from this AI QA & Security Tester template. Playwright E2E, OWASP probes, and release gate rules are pre-loaded.
Click on “Hire”
Activate Maya instantly with $0 template fee and 1,000 free execution credits. Pair her with Noah (AI Software Engineer) for closed-loop bug fixes.
Connect Tools — That's It!
Connect GitHub/GitLab, Jira/Linear, Slack, and your staging environment URL. Maya starts testing every commit and deploy automatically.
Need Custom Security Policies or Compliance Gates?
Want a ready-made QA & security tester? Simply click Hire and connect your repo and staging URL—it starts working immediately. Custom prompts are only needed for domain-specific compliance checks, custom auth flows, or bespoke load profiles.
Who Benefits Most from Maya?
Designed for SaaS teams, CISOs, QA leads, and digital agencies shipping software rapidly without sacrificing reliability or security.
Fast-Moving Startups
Ship multiple deploys a day with automated E2E QA and OWASP security coverage before hiring a full QA department.
AppSec & Compliance Teams
Replace annual point-in-time pentests with continuous DAST, SAST, secret scanning, and audit-ready release logs.
QA & Release Managers
Eliminate manual regression checklists, flaky selector maintenance, and delayed Friday release sign-offs.
FinTech & Agencies
Verify multi-tenant isolation, payment flows, and client deliverables with signed QA and security reports on every release.
Frequently Asked Questions
Common questions about Maya's E2E testing, OWASP security probes, load testing, and release gate guardrails.
Lock Down Quality & Security with Maya Today
Hire your autonomous AI QA & Security Tester for $0 template fee. Test every UI flow, API, and OWASP boundary—and pair her with Noah (AI Software Engineer) to ship fixes automatically.