Catherine • Autonomous SAP GRC & Security Lead Catherine • Autonomous SAP GRC & Security Lead

Real-Time SoD Risk Analysis & Firefighter Logging for
Enterprise SAP S/4HANA Governance, Risk & Compliance

Catherine stops Segregation of Duties (SoD) violations before role assignment, audits Firefighter (EAM) emergency sessions, enforces least-privilege PFCG roles, and automates SOX 404 access reviews 24/7.

SoD Risk Analysis • Firefighter Audit Least-Privilege Roles • 1,000 Free Credits Included
Catherine
Catherine AI SAP GRC Specialist
SAP GRC Access Control 12.0 • S/4HANA Security
Active Shift

"Catherine, analyze access request #ARM-9014: user requests role Z_SAP_FI_AP_CLERK (Vendor Payment) while currently holding Z_SAP_MM_BUYER (Purchase Order Creation)."

YOU
Catherine
SAP GRC Access Risk Analysis (ARA) Verified • 0.28s

Running real-time SoD risk simulation against corporate rulebook:

Critical SoD Conflict Detected: Rule ID #P001 (Create Purchase Orders [ME21N] vs. Pay Vendor Invoices [F110]).
Request Blocked: Prevented unauthorized combination that would allow fraudulent disbursement without secondary approval.
Least-Privilege Alternative: Proposed restricted display role Z_SAP_FI_AP_DISP (FB03 display only) to satisfy operational need.
Audit Dossier Generated: Sent risk explanation to Internal Audit and requestor's manager on Slack #grc-security.
Certified Clean Core Execution Complete 100% Autonomous
Natural Language • Real SAP BAPIs & Certified OData 1,000 Free Credits
1
SoD Simulation
Pre-Assignment Risk Check
2
Emergency EAM Logs
Automated T-Code Audit
3
SOX 404 Readiness
Cryptographic Access Proof
4
$0 Template Fee
1,000 Free Credits
AI EMPLOYEE VS AI AGENT

What is an AI SAP Employee? How It's Different From a Basic Tool

An AI Employee is not just a reactive bot. It is an autonomous, multi-agent coworker with persistent operational memory that executes end-to-end business workflows on scheduled shift cycles across your enterprise SAP landscape.

Standard AI Bot / RPA Script

Single-Task • Rigid • No ERP Context
Basic Automation

A standard RPA macro or generic chatbot only copies fields into GUI forms, but breaks whenever transaction layouts change, business exceptions occur, or partner schemas update.

  • No Multi-Step Reasoning: Cannot evaluate business tolerances, cross-reference custom tables, or resolve conflicting requirements.
  • Zero Long-Term Memory: Forgets historical supplier trends, vendor performance, or past audit adjustments after each call.
  • No Proactive Healing: Fails silently and requires constant human babysitting to resolve failed runs.
Leaves enterprise teams bogged down in manual operations
RHINOAGENTS AI EMPLOYEE
Catherine

Catherine • AI SAP GRC Specialist

Multi-Agent • Certified Clean Core • 24/7 Shifts

Catherine operates as an autonomous enterprise specialist. Equipped with specialized sub-agents, persistent memory, and deterministic safety guardrails, Catherine executes end-to-end ERP operations with zero human delay.

  • Multi-Agent Team Orchestration: Deploys autonomous sub-agents to monitor, validate, execute BAPIs, and alert human reviewers.
  • Certified Clean Core Architecture: Runs 100% via standard RFCs, NetWeaver OData, and SAP BTP—no custom code required.
  • Persistent Operational Memory: Remembers past exceptions, enterprise tolerances, vendor master rules, and auditor preferences.
Automates over 80% of repetitive operational workloads
Production Skills In Template

What We Have In This Template

Helena comes pre-configured with 8 production-grade autonomous capabilities across SAP GRC Access Control, Segregation of Duties (SoD), and emergency access auditing.

Real-Time SoD Conflict Analysis
SoD Risk GRC-01

Real-Time SoD Conflict Analysis

Evaluates new user role assignments against global Segregation of Duties matrices to block toxic authorization combinations.

The Problem: Granting users toxic role combinations (e.g. creating vendor + releasing payment) creates severe fraud risks and audit failures.
Why This Feature Helps: Runs proactive risk simulations before access is provisioned, blocking conflicting authorizations and requiring compensating controls.
  • Pre-assignment risk simulation
  • Toxic combination prevention
Firefighter Emergency Log Auditing
Emergency Access GRC-02

Firefighter Emergency Log Auditing

Analyzes elevated privilege sessions (EAM / Firefighter), correlating T-Codes executed with approved change tickets.

The Problem: IT administrators use elevated Firefighter (EAM) IDs without proper post-session audits, leaving unauthorized changes undetected.
Why This Feature Helps: Automatically reviews Firefighter activity logs, correlating executed transactions against approved emergency change tickets.
  • Unapproved T-Code execution alerts
  • Firefighter session replay analysis
Periodic User Access Review (UAR)
Access Review GRC-03

Periodic User Access Review (UAR)

Coordinates periodic manager recertification campaigns, identifying inactive users and removing obsolete authorizations.

The Problem: Managers rubber-stamp annual access recertification spreadsheets without reviewing actual usage, allowing unauthorized access to persist.
Why This Feature Helps: Tracks actual transaction execution, highlighting unused authorizations and guiding managers through automated revocation workflows.
  • Manager recertification workflows
  • Automated role revocation requests
Privilege Creep & Inactive User Detection
Privilege Creep GRC-04

Privilege Creep & Inactive User Detection

Monitors employees transferring between departments, identifying legacy role authorizations that should be revoked.

The Problem: Employees changing departments retain historical permissions, accumulating broad, dangerous security profiles over time.
Why This Feature Helps: Cross-references HR master data with SAP user profiles, automatically triggering removal of obsolete departmental roles.
  • Cross-department role auditing
  • Inactive account lock triggering
Continuous Control Monitoring (CCM)
Control Monitor GRC-05

Continuous Control Monitoring (CCM)

Runs automated background audits on sensitive configuration tables (e.g. payment terms, vendor bank changes) in S/4HANA.

The Problem: Critical business configuration tables (e.g. payment terms, vendor bank details) can be altered without triggering standard audit logs.
Why This Feature Helps: Continuously monitors sensitive table updates in real time, alerting compliance officers to unauthorized configuration alterations.
  • Sensitive table alteration alerts
  • Vendor bank change audit logs
Composite & Single Role Remediation
Role Design GRC-06

Composite & Single Role Remediation

Identifies over-privileged roles, recommending clean role splits that segregate transaction codes and authorization objects.

The Problem: Legacy SAP roles contain broad wildcards (*) and excessive transaction codes that make clean Segregation of Duties impossible.
Why This Feature Helps: Analyzes role definitions and user execution logs to recommend targeted role splits that remove toxic authorization overlap.
  • Role authorization optimization
  • Broad wildcard (*) removal checks
External Audit Evidence Generation
Audit Readiness GRC-07

External Audit Evidence Generation

Packages cryptographically stamped audit trails of role approvals, firefighter logs, and risk mitigations for Big 4 auditors.

The Problem: Preparing for annual SOX and external audit reviews requires hundreds of hours manually compiling spreadsheets and change logs.
Why This Feature Helps: Produces cryptographically stamped audit evidence packages with one click, providing complete traceability for Big 4 auditors.
  • One-click SOX compliance bundles
  • Immutable audit evidence exports
Critical T-Code Access Violation Guard
Critical T-Codes GRC-08

Critical T-Code Access Violation Guard

Maintains real-time perimeter defense around sensitive transactions (SCC4, SE16N, SM30, SU01) to block unauthorized execution.

The Problem: Unauthorized execution of dangerous transaction codes (SCC4, SE16N, SM30, SU01) can bypass all internal business controls.
Why This Feature Helps: Enforces perimeter defense on sensitive T-Codes, logging all execution attempts and alerting the CISO to policy breaches.
  • Direct table edit attempt alerts
  • Immediate CISO notification triggers
PERFORMANCE BENCHMARK

Manual ERP Operations vs. Autonomous Catherine AI

See how automating complex SAP workflows with RhinoAgents eliminates backlogs and human bottlenecks.

Operation Area Manual Process Catherine • Autonomous AI
SoD Conflict Detection Discovered months later during external audit reviews Prevented in real time before role assignment via automated simulation
Firefighter Session Audits Weeks of manual log review by overloaded security teams Automated log parsing & sensitive transaction verification within minutes
Quarterly Access Reviews Hundreds of manual Excel spreadsheets sent via email Automated campaigns with one-click manager sign-off workflows
PFCG Role Authorizations Broad wildcards (*) granting excessive user privileges Continuous least-privilege role scanning and remediation
Audit Defense & SOX Proof Panicked scramble to gather scattered audit evidence Permanent, immutable, cryptographically verifiable compliance trails
AUTONOMOUS EXECUTION FLOW

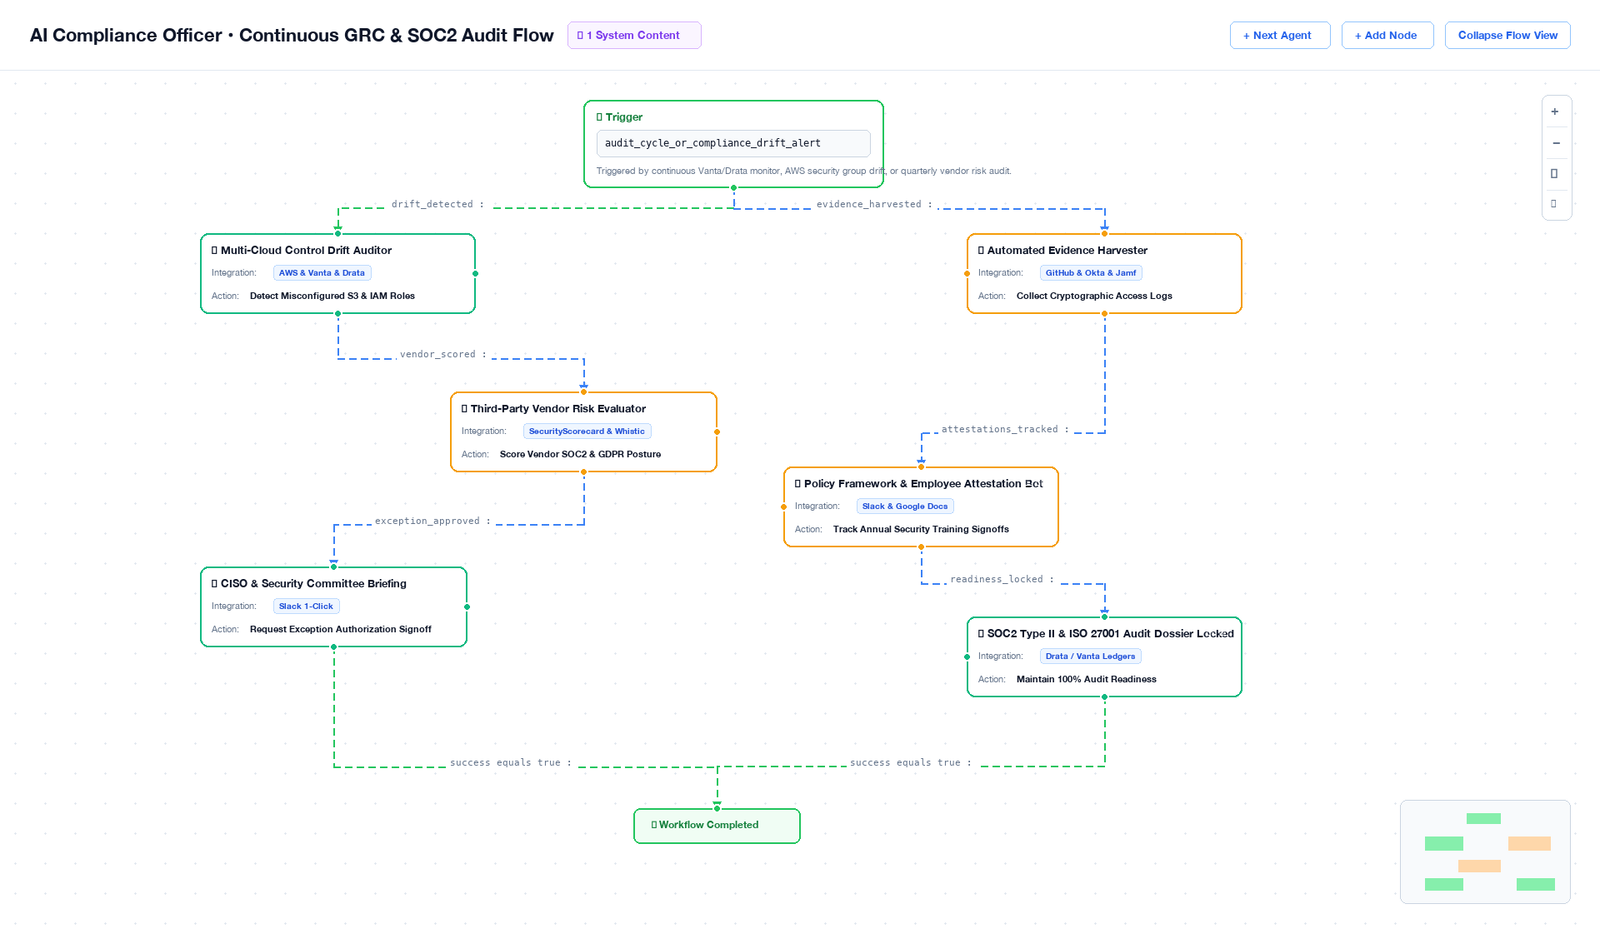
End-to-End Autonomous SAP Architecture

How Catherine coordinates data ingestion, deterministic validation, SAP BAPI posting, and audit reporting.

Catherine Workflow Architecture
ENTERPRISE SECURITY & COMPLIANCE

Certified Clean Core Architecture. Zero ERP Modifications.

RhinoAgents adheres strictly to SAP Clean Core principles. Catherine communicates exclusively through certified RFCs, NetWeaver Gateway OData services, and SAP BTP endpoints with full transactional rollback safety.

SOC 2 Type II Certified

AES-256 encryption at rest, TLS 1.3 in transit, and granular audit trails.

PFCG Role Segregation

Operates strictly within assigned standard SAP authorizations.

sap_clean_core_compliance.json
100% CLEAN CORE
{
  "system": "SAP GRC Access Control 12.0 • S/4HANA Security",
  "integration_standard": "Certified SAP RFC / OData v4",
  "clean_core_compliant": true,
  "transaction_rollback": "Enabled (BAPI_TRANSACTION_ROLLBACK)",
  "audit_trail": "Cryptographically Stamped & Immutable",
  "sox_dual_signoff": "Configured via Slack & MS Teams",
  "data_residency": "Customer VPC / Zero-Data-Retention"
}
RAPID TIME TO VALUE

Deploy Catherine to Your Team in 4 Simple Steps

No 6-month consulting integration projects. Go live with autonomous execution in days.

01

Connect SAP Securely

Connect your SAP S/4HANA or ECC instance using standard RFC connection credentials or NetWeaver Gateway OData services.

Estimated: 15 minutes
02

Define Scope & Scope Orgs

Specify participating Company Codes, Plants, Purchasing/Sales Orgs, and document types in scope.

Estimated: 25 minutes
03

Set Safety Guardrails

Configure maximum automated value thresholds, tolerance keys, and Slack/Teams human approval requirements.

Estimated: 20 minutes
04

Launch Autonomous Shift

Test in Simulation Mode to review proposals before activating live BAPI execution. Start saving hundreds of hours immediately.

Ready to Run 24/7
CLEAR ANSWERS

Frequently Asked Questions About Catherine

Everything your enterprise IT leadership, business process owners, and auditors need to know.

Catherine compares user role assignments against a matrix of conflicting authorizations (e.g., maintaining vendor master data vs. executing payments, or creating POs vs. clearing invoices) using SAP GRC Access Risk Analysis principles.
Yes. Catherine ingests Firefighter session logs, cross-references transaction codes and table modifications against approved emergency incident tickets (e.g. ServiceNow), and flags any suspicious activity.
Yes. Catherine audits both traditional back-end PFCG composite/single roles and modern Fiori tile catalogs and business catalogs in S/4HANA.
Catherine identifies users holding sensitive access, groups them by department manager, distributes interactive recertification requests via Slack or MS Teams, and deprovisions revoked access automatically.
No. Catherine follows strict governance rules: all proposed role updates and revocations are audited and require human-in-the-loop authorization before execution.
Yes. Catherine connects with enterprise IAM systems via standard SCIM and REST APIs to maintain identity synchronization.
Instant Onboarding • No Implementation Fee

Deploy Catherine to Your SAP Team Today

Join hundreds of enterprise companies automating complex operational workflows with RhinoAgents. Start with $0 template fee and 1,000 free execution credits.

No credit card required 1,000 free execution credits Cancel or reconfigure anytime