AI Compliance Employee Architecture • SOC 2, HIPAA & ISO 27001 Certified • Zero Per-Seat Fees

Hire a Ready-Made AI Compliance Employee — or build a custom one in minutes

Stop scrambling through spreadsheets and evidence screenshots during annual audits. Deploy an autonomous AI Chief Compliance Officer that oversees 8 specialized sub-agents to continuously audit policy controls, collect vendor security certifications, monitor GDPR/HIPAA compliance, and sync Vanta/Drata 24/7.

No credit card required Live within 15 minutes SOC 2 & GDPR compliant Native CRM & App integrations Zero per-seat user tax
8 Sub-Agents
Autonomous GRC audit squad
100%
Continuous real-time evidence audit
-80%
Annual audit preparation time
Credit-Based
1,000 free credits • Plans from $20/mo
Live Interactive Console & Architecture

Primary AI Employee: Chief Compliance Officer & GRC Director

Experience how an autonomous primary AI Employee orchestrates 8 specialized sub-agents to vet data, enforce business rules, and trigger human approval gates in real time.

Live Orchestration Console

Active Regulatory Compliance Desk • Enterprise GRC Evidence Stream

Active Pipeline Mode Enterprise Stack Synced
GRC
Continuous SOC 2 & HIPAA Audit • Control #CC6.1 Review • Control: Multi-Factor Authentication & Access Reviews • Scope: Production Cloud
Status: 98% Evidence Verified • Gap Detected: 2 Contractor Accounts Missing Quarterly Sign-Off
Audit Readiness: 98%
Evidence Collector:
Gathered Okta MFA logs & AWS IAM policies
Vendor Assessor:
Extracted SOC 2 report from new cloud provider
Drata Sync:
Updated control #CC6.1 evidence in Drata GRC
Governance Gate: Material compliance control failures prompt Chief Compliance Officer Slack alert.
Primary AI Employee: Chief Compliance Officer & GRC Director

Autonomous Regulatory Governance & Risk Controller

Monitors enterprise compliance frameworks (SOC 2, ISO 27001, HIPAA, GDPR), coordinates 8 audit sub-agents, detects non-compliant cloud configurations, and prepares auditor-ready dossiers.

Autonomous Orchestrator Active v2.4
Continuous Evidence Collector
Automated Evidence
Vendor Security & SOC 2 Evaluator
Vendor SOC 2 Parsing
Quarterly Access Review Orchestrator
User Access Reviews
GDPR / CCPA Subject Request (DSR) Agent
Right to Be Forgotten
GRC Tool Two-Way Sync (Vanta/Drata)
Vanta & Drata
Security Policy & SOP Generator
InfoSec Policy Drafting
Cloud Misconfiguration Sentry
Cloud Security Posture
Compliance FAQ & Questionnaire Copilot
Security Questionnaires
Rule Logic Preview Unencrypted S3 buckets auto-quarantine within 60s • Access reviews mandatory every 90 days • GDPR deletion requests execute in 24h
Customize Rules
Flexible Deployment Spectrum

Three Ways to Put AI to Work in Your Team

Whether you want an instant out-of-the-box employee, want to adapt existing business rules, or need a fully bespoke custom AI employee, RhinoAgents gives you complete flexibility.

Option 1 • Instant Deployment

Hire a Ready-Made Compliance Employee

Deploy an out-of-the-box AI Compliance Officer equipped with all 8 sub-agents. Integrates directly with Vanta, Drata, Secureframe, AWS, Okta, and GitHub in minutes.

  • All 8 specialized regulatory governance & audit sub-agents enabled
  • Pre-mapped control frameworks for SOC 2, ISO 27001, HIPAA & GDPR
  • Native integrations with Vanta, Drata & Secureframe
Hire Ready-Made Employee
Most Popular
Option 2 • No-Code Customization

Change Rules & Business Logic

Keep the ready-made employee architecture, but adapt the logic to your exact business operations. Adjust scoring thresholds, set custom knockout questions, alter tone, and define approval triggers.

  • Modify scoring rubrics & operational criteria
  • Set automated knockout filters for zero bad fits
  • Configure Slack human-in-the-loop review gates
Learn How to Edit Rules
Option 3 • Bespoke AI Employee

Create a Custom AI Employee

Build a custom AI compliance employee tailored for SEC/FINRA investment regulations, FedRAMP government authorization, or PCI-DSS Level 1 payment security.

  • Custom role identity, persona & voice
  • Select which specialized sub-agents work under it
  • Connect to proprietary databases & webhooks
Build Custom AI Employee
Bespoke Creation Wizard

How to Create Your Custom AI Employee in 4 Steps

Need a purpose-built AI employee tailored to your organization? Use our intuitive step-by-step studio to define identity, channels, orchestrated sub-agents, and task execution logic.

Step 1 • Identity Configuration

Define Role Name, Avatar & Persona

Name your AI employee, upload or select a brand avatar, define its job title, and establish its core personality traits. Configure whether it communicates with a consultative corporate tone, an energetic sales cadence, or a friendly customer care voice.

Role Name & Title: e.g., "FinTech & Healthcare Compliance Lead"
Persona Definition: Set brand voice guidelines, communication policies, and greeting formats.
Avatar & Bio: Establish internal and customer-facing profile visuals.
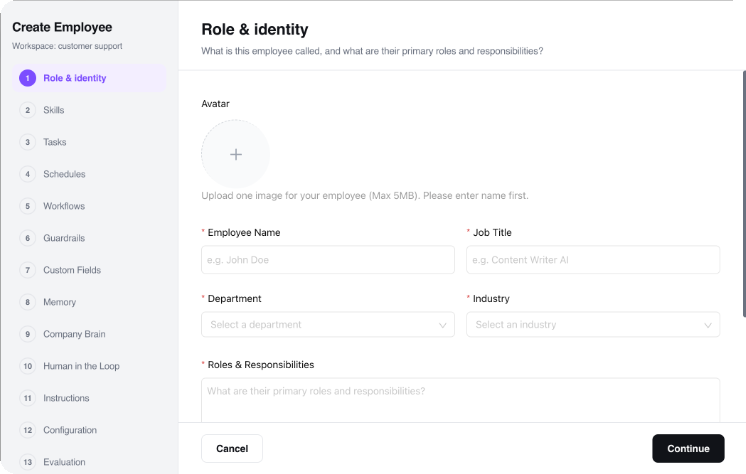
Step 1 Identity Studio
Autonomous Multi-Agent Workflow

How Sub-Agents Collaborate Under the AI Employee

Sub-agents do not operate as disconnected single-purpose bots. They operate as a synchronized squad orchestrated by the primary AI Employee, exchanging context and data in real time.

1

Signal & Intake

Inquiry or record is ingested from web chat, email, form submission, or webhook. Primary AI Employee verifies context and dispatches it to the Intake sub-agent.

Trigger: Signal Received
2

Enrichment & Vetting

Data is parsed against your custom rubrics. Sub-agents verify external databases, enrich missing parameters, and calculate objective qualification scores.

Logic: Custom Rubrics
3

Gate Evaluation

Scores meeting your auto-advance threshold proceed immediately. Borderline cases generate an executive summary card to a designated Slack channel for human 1-click review.

Security: Human-in-the-Loop
4

Action & 360° Sync

Sub-agents book calendar invites, trigger confirmation notifications, and write full audit logs into your CRM, ERP, and database systems automatically.

Output: Closed-Loop Execution
Modular Sub-Agent Squad

8 Ready-Made Sub-Agents at Your Service

Each sub-agent is an autonomous specialist. Use them together under the Primary AI Employee or configure individual rules, knockouts, and triggers for each.

Sub-Agent 01

Continuous Evidence Collector

Pulls automated screenshots, API logs, and configuration proofs from AWS, GitHub, Okta, and Jamf to satisfy audit controls.

Trigger: Scheduled daily audit cron
Output: Timestamped evidence bundle
Automated Evidence Vanta / Drata Sync
Sub-Agent 02

Vendor Security & SOC 2 Evaluator

Parses incoming vendor SOC 2 Type II reports, ISO certifications, and bridge letters, flagging unmitigated vendor risk.

Trigger: Vendor security doc uploaded
Output: Third-party risk assessment
Vendor SOC 2 Parsing Third-Party Risk
Sub-Agent 03

Quarterly Access Review Orchestrator

Generates employee and contractor access lists, sends 1-click verification prompts to managers, and flags orphaned accounts.

Trigger: 90-day review cycle milestone
Output: Completed access review ledger
User Access Reviews Orphaned Account Purge
Sub-Agent 04

GDPR / CCPA Subject Request (DSR) Agent

Handles 'Right to Be Forgotten' and data export requests, querying databases to purge customer PII within statutory deadlines.

Trigger: DSR / GDPR request submitted
Output: PII deletion verification receipt
Right to Be Forgotten GDPR & CCPA Deadlines
Sub-Agent 05

GRC Tool Two-Way Sync (Vanta/Drata)

Updates control statuses, tests passing proofs, and logs exceptions directly in Vanta, Drata, or Secureframe.

Trigger: Control test execution
Output: Synchronized GRC control record
Vanta & Drata Secureframe Integration
Sub-Agent 06

Security Policy & SOP Generator

Drafts customized Information Security Policies (ISPs), Incident Response Plans, and Business Continuity SOPs following ISO standards.

Trigger: Policy revision requirement
Output: Auditor-compliant policy draft
InfoSec Policy Drafting ISO 27001 Alignment
Sub-Agent 07

Cloud Misconfiguration Sentry

Detects unencrypted databases, publicly accessible cloud buckets, and disabled audit logging, prompting DevOps to patch gaps.

Trigger: AWS/GCP configuration drift
Output: Security misconfiguration alert
Cloud Security Posture S3 Bucket Encryption
Sub-Agent 08

Compliance FAQ & Questionnaire Copilot

Fills out complex 200+ question enterprise security questionnaires (CAIQ, SIG, custom RFPs) in minutes using verified policy citations.

Trigger: Security questionnaire received
Output: Completed security questionnaire
Security Questionnaires CAIQ & SIG Response
No-Code Rule Customization

How to Change Rules & Customize Logic

You never have to accept a rigid black-box AI. Every scoring weight, knockout condition, tone guideline, and approval gate can be altered in seconds using visual toggles or natural language.

1. Adjust Scoring Weights

Use visual percentage sliders to weight qualification rubrics (e.g. 40% Fit Criteria, 30% Budget/Timeline, 20% Tech Stack, 10% Profile Quality).

Core Fit:40%
Authority / Budget:30%

2. Set Mandatory Knockout Criteria

Add non-negotiable prerequisite rules. If an inquiry fails any knockout criteria, it is politely handled with an automated response without wasting your team's time.

Minimum budget threshold met
Corporate business email domain
Operating in serviceable geographic territory

3. Set Human Approval Thresholds

Define exact score brackets that trigger instant execution versus those requiring human team sign-off via Slack or email.

• Score ≥ 85: Auto-execute
• Score 70-84: Slack Team 1-Click Gate
• Score < 70: Polite automated routing
Natural Language Rule Modification

Or Simply Edit Rules in Plain English

Zero Code Required
// Type plain English prompt to change rules:
"Unencrypted S3 buckets auto-quarantine within 60s • Access reviews mandatory every 90 days • GDPR deletion requests execute in 24h"
RhinoAgents Logic Engine Compiles:
  • • Evaluates criteria ≥ 200 units → Rule Tag: TIER_1_VIP
  • • Trigger action → CALENDAR_SYNC_SENIOR_PANEL
  • • Webhook → SLACK_DISPATCH(#sales-leads)
Applied instantly across all 8 sub-agents Live Status: Active
Ideal Fit

Built for Modern Teams Across Every Scale

From agile high-velocity startups to established enterprise organizations, deploy an autonomous AI Compliance Employee tailored to your operational velocity.

Corporate Legal

General Counsel & In-House Legal

Accelerate NDA, vendor agreement, and standard commercial paper review cycles without outside counsel.

75% Faster Review
Boutique Law Firms

Specialized Law Practices

Automate matter intake, precedent case research, and client document collection with bank-grade security.

Zero Intake Delay
Regulated Tech

FinTech, HealthTech & AI Scaleups

Enforce continuous compliance tracking, vendor risk assessments, and cryptographic audit records.

SOC 2 & GDPR Proof
Procurement Teams

Enterprise Procurement Desks

Identify unfavorable liability caps, indemnification traps, and payment term drifts in vendor drafts.

Risk Mitigation
Proven Operational ROI

Measurable Advantages for Modern Organizations

Replacing administrative manual labor with an autonomous AI Compliance Employee delivers direct returns on execution speed, operational accuracy, and staffing overhead.

75% Faster Contract Cycles

Extract critical clauses, indemnity terms, and payment schedules from counterparties in seconds.

100% Redline Playbook Adherence

Enforces company-approved standard positions and flags non-conforming clauses automatically.

Zero Audit & Compliance Gaps

Maintains complete cryptographic version histories, approval timestamps, and regulatory logs.

Drastic Legal Spend Reduction

Handle standard commercial paper internally using flexible execution credits with plans starting at $20/month.

Coordinated Legal Ops Squad

8 sub-agents handle contract intake, redlining, compliance auditing, risk scoring, and cloud filing.

Native Legal Cloud Sync

Direct integration with Ironclad, Clio, DocuSign, SharePoint, Google Drive, and Microsoft Word.

Ecosystem Connectors

Native Integrations with Your Existing Stack

Connect your CRM, messaging channels, databases, and enterprise tools in seconds. The AI employee synchronizes updates automatically without changing your team's workflow.

Clio Ironclad DocuSign NetDocuments SharePoint LexisNexis Google Drive Microsoft Word Adobe Sign Outlook Slack 400+ More Integrations →
Frequently Asked Questions

Got Questions? We Have Answers.

Everything you need to know about hiring, customizing, and scaling autonomous AI employees.

It connects to your cloud providers, code repos, and identity platforms (AWS, GitHub, Okta, Jamf), capturing cryptographic proofs and configuration snapshots required by auditors.

We provide native integrations with Vanta, Drata, Secureframe, Hyperproof, Sprinto, and Tugboat Logic.

Yes. Our Questionnaire Copilot sub-agent indexes your approved security policies, SOC 2 reports, and architecture diagrams to answer SIG, CAIQ, and custom questionnaires in minutes.

Yes. Every newly drafted policy, exception waiver, or auditor disclosure requires 1-click human authorization before sealing.

RhinoAgents operates on a transparent credit-based model with zero per-seat human fees. You start with 1,000 free execution credits on our Free Trial ($0). Monthly plans start at $20/month (Starter: 10,000 credits/mo), $49/month (Pro: 50,000 credits/mo), and $99/month (Business: 150,000 credits/mo). Credits are consumed based on task complexity (such as research, data processing, workflow orchestration, communication, or CRM/ERP syncing). Unlimited human team members can access and collaborate with the AI employee without paying user seat penalties.

RhinoAgents pays for 100% of the underlying AI model costs (LLM tokens for GPT-4o, Claude 3.5 Sonnet, Gemini, etc.) and cloud computing infrastructure—all covered directly by your monthly credit allotment. You never need to supply your own OpenAI or Anthropic API keys. The customer is only responsible for their own external third-party software subscriptions and tool accounts (such as your existing CRM, ATS, Twilio, WhatsApp Business API, ERP, or cloud accounts). RhinoAgents connects seamlessly via 1-click native integrations with zero markup.

Get Started in Minutes

Put Your Autonomous AI Compliance Employee to Work Today

Deploy in 15 minutes. Connect your CRM, email, and tools with 1-click connectors. Experience the power of an orchestrated AI team without adding headcount.

No credit card required 15-Minute Quick Setup SOC 2 & GDPR Compliant No Per-Seat Human Fees