Stop letting alert fatigue and delayed incident response expose your enterprise to breaches. Deploy an autonomous AI Security Operations (SOC) Lead that oversees 8 specialized sub-agents to triage SIEM alerts in seconds, correlate threat intelligence, isolate compromised devices, and sync Jira/Splunk 24/7.
Experience how an autonomous primary AI Employee orchestrates 8 specialized sub-agents to vet data, enforce business rules, and trigger human approval gates in real time.
Maintains corporate security baseline rules, orchestrates 8 threat analysis sub-agents, enforces isolation containment policies, and pages human on-call security engineers.
Whether you want an instant out-of-the-box employee, want to adapt existing business rules, or need a fully bespoke custom AI employee, RhinoAgents gives you complete flexibility.
Deploy an out-of-the-box AI SOC Lead equipped with all 8 sub-agents. Integrates directly with Splunk, CrowdStrike, SentinelOne, Microsoft Sentinel, and Okta in 15 minutes.
Keep the ready-made employee architecture, but adapt the logic to your exact business operations. Adjust scoring thresholds, set custom knockout questions, alter tone, and define approval triggers.
Build a custom AI security employee tailored for AWS/GCP cloud security posture management (CSPM), Kubernetes container audits, or zero-trust identity.
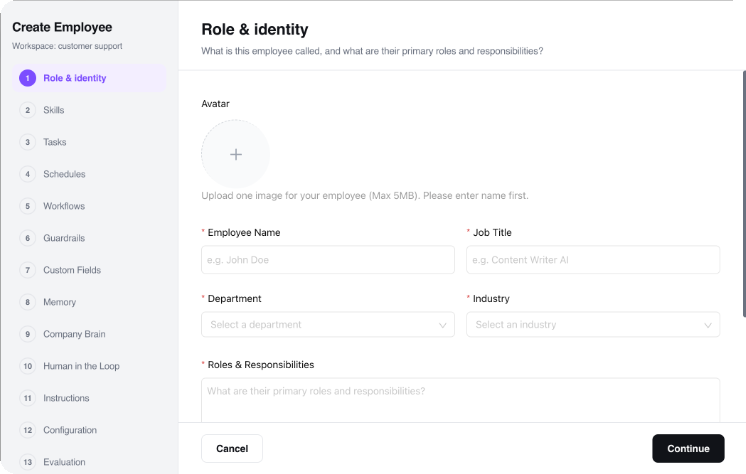
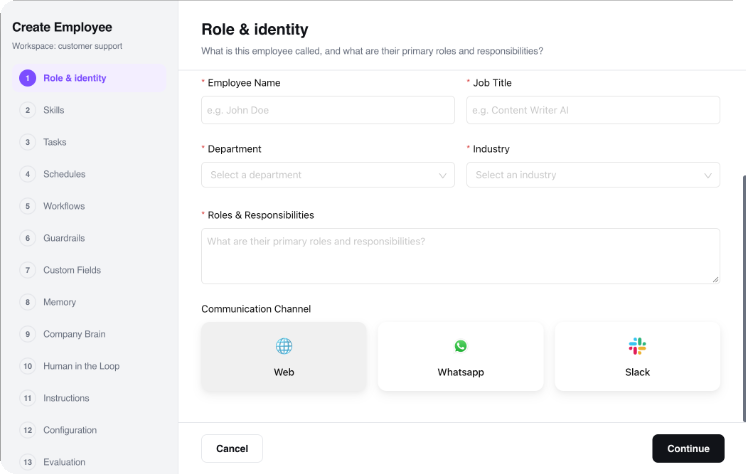
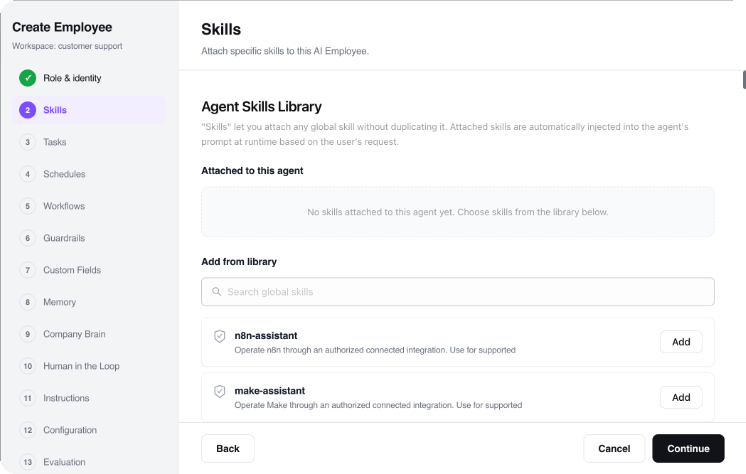
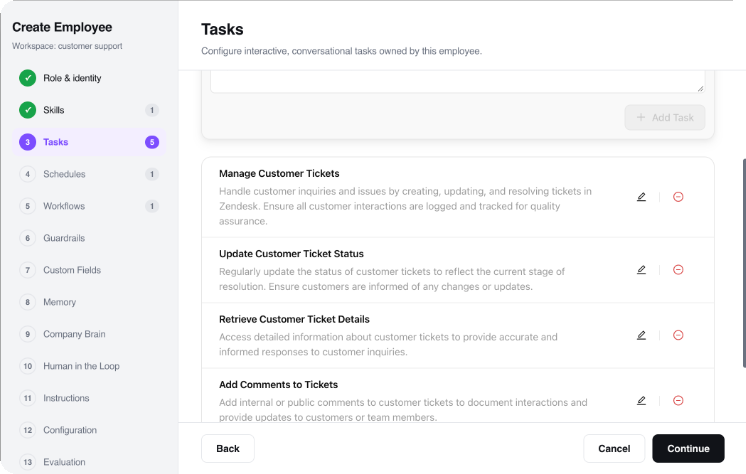
Need a purpose-built AI employee tailored to your organization? Use our intuitive step-by-step studio to define identity, channels, orchestrated sub-agents, and task execution logic.
Name your AI employee, upload or select a brand avatar, define its job title, and establish its core personality traits. Configure whether it communicates with a consultative corporate tone, an energetic sales cadence, or a friendly customer care voice.
Sub-agents do not operate as disconnected single-purpose bots. They operate as a synchronized squad orchestrated by the primary AI Employee, exchanging context and data in real time.
Inquiry or record is ingested from web chat, email, form submission, or webhook. Primary AI Employee verifies context and dispatches it to the Intake sub-agent.
Data is parsed against your custom rubrics. Sub-agents verify external databases, enrich missing parameters, and calculate objective qualification scores.
Scores meeting your auto-advance threshold proceed immediately. Borderline cases generate an executive summary card to a designated Slack channel for human 1-click review.
Sub-agents book calendar invites, trigger confirmation notifications, and write full audit logs into your CRM, ERP, and database systems automatically.
Each sub-agent is an autonomous specialist. Use them together under the Primary AI Employee or configure individual rules, knockouts, and triggers for each.
Filters noisy alerts from Splunk, Microsoft Sentinel, or Datadog, correlating signals to eliminate 94%+ of benign false positives.
Cross-references suspicious IPs, domains, and file hashes against VirusTotal, AlienVault OTX, and MITRE ATT&CK frameworks.
Analyzes reported employee emails, inspecting SPF/DKIM headers, sandboxing attachments, and pulling hidden tracking URLs.
Triggers rapid network containment via CrowdStrike Falcon or SentinelOne APIs to stop malware lateral movement in under 10 seconds.
Detects impossible travel or credential stuffing, terminating active OAuth sessions in Okta/Azure AD and enforcing password resets.
Pushes real-time IP blacklists and rate-limiting rules to Cloudflare, AWS WAF, or Palo Alto Networks to block active DDoS and web attacks.
Scans internal repositories and container registries for high-severity CVEs, prioritizing patch tickets based on real-world exploitability.
Compiles comprehensive forensic timelines, evidence artifacts, and post-mortem reports for executive leadership and compliance auditors.
You never have to accept a rigid black-box AI. Every scoring weight, knockout condition, tone guideline, and approval gate can be altered in seconds using visual toggles or natural language.
Use visual percentage sliders to weight qualification rubrics (e.g. 40% Fit Criteria, 30% Budget/Timeline, 20% Tech Stack, 10% Profile Quality).
Add non-negotiable prerequisite rules. If an inquiry fails any knockout criteria, it is politely handled with an automated response without wasting your team's time.
Define exact score brackets that trigger instant execution versus those requiring human team sign-off via Slack or email.
TIER_1_VIPCALENDAR_SYNC_SENIOR_PANELSLACK_DISPATCH(#sales-leads)From agile high-velocity startups to established enterprise organizations, deploy an autonomous AI Cybersecurity Employee tailored to your operational velocity.
Autonomous telemetry inspection, root-cause correlation, and auto-remediation runbooks across microservices.
Cut alert noise by 70%, correlate cross-service traces, and trigger instant PagerDuty escalations for genuine P0s.
Block prompt injection attacks, neutralize credential leak attempts, and maintain continuous GDPR logs.
Provide 24/7 autonomous client monitoring, ticket classification, and automated node failovers.
Replacing administrative manual labor with an autonomous AI Cybersecurity Employee delivers direct returns on execution speed, operational accuracy, and staffing overhead.
Detect infrastructure anomalies, latency spikes, and security drifts in seconds across telemetry.
Intelligent deduplication filters noise and only alerts your on-call engineers for genuine P0/P1s.
Executes pre-approved remediation scripts, spins down degraded nodes, and logs recovery steps.
Security sub-agents inspect inputs before LLMs process them, protecting proprietary company data.
Telemetry monitoring, anomaly detection, root-cause triage, and post-mortem creation working as one.
Full bidirectional connectivity with Langfuse, Datadog, PagerDuty, Slack, Jira, and GitHub.
Connect your CRM, messaging channels, databases, and enterprise tools in seconds. The AI employee synchronizes updates automatically without changing your team's workflow.
Everything you need to know about hiring, customizing, and scaling autonomous AI employees.
It aggregates related alerts across SIEM, EDR, and identity feeds, correlating them against threat intelligence databases to eliminate false positives and present only high-fidelity incidents.
We support native integrations with CrowdStrike Falcon, SentinelOne, Microsoft Defender / Sentinel, Splunk, Datadog Security, Okta, and Cloudflare.
Yes. You define policy thresholds: low-risk actions (like isolating a single workstation running known ransomware) can execute automatically, while perimeter changes require human 1-click confirmation.
Yes. All security telemetry is processed in an encrypted, single-tenant environment with zero third-party model retention.
RhinoAgents operates on a transparent credit-based model with zero per-seat human fees. You start with 1,000 free execution credits on our Free Trial ($0). Monthly plans start at $20/month (Starter: 10,000 credits/mo), $49/month (Pro: 50,000 credits/mo), and $99/month (Business: 150,000 credits/mo). Credits are consumed based on task complexity (such as research, data processing, workflow orchestration, communication, or CRM/ERP syncing). Unlimited human team members can access and collaborate with the AI employee without paying user seat penalties.
RhinoAgents pays for 100% of the underlying AI model costs (LLM tokens for GPT-4o, Claude 3.5 Sonnet, Gemini, etc.) and cloud computing infrastructure—all covered directly by your monthly credit allotment. You never need to supply your own OpenAI or Anthropic API keys. The customer is only responsible for their own external third-party software subscriptions and tool accounts (such as your existing CRM, ATS, Twilio, WhatsApp Business API, ERP, or cloud accounts). RhinoAgents connects seamlessly via 1-click native integrations with zero markup.
Deploy in 15 minutes. Connect your CRM, email, and tools with 1-click connectors. Experience the power of an orchestrated AI team without adding headcount.